What does a Information Security Officer do?
An Information Security Officer plays a critical role in protecting an organization's sensitive data. This person manages the security policies and procedures to safeguard the company's information. They assess risks, create security plans, and make sure that all staff follow security protocols. An Information Security Officer conducts regular audits to ensure that systems are safe from threats. They respond to security breaches and work to minimize any damage. This role requires strong analytical skills and a deep understanding of cybersecurity.
The Information Security Officer works closely with other departments to ensure everyone understands the importance of security. They provide training and resources to staff to promote a culture of security. They also stay updated on the latest security trends and technologies. An Information Security Officer needs to be detail-oriented and proactive. They must be able to identify potential risks before they become problems. This role is essential for maintaining the trust and confidence of clients and stakeholders. It ensures that the organization’s data remains protected and secure.
How to become a Information Security Officer?
To become an Information Security Officer, one should follow a structured path. This role requires a combination of skills and qualifications that ensure data protection and security. Below are the steps to successfully pursue this career.
First, obtain a relevant degree. Most employers prefer a bachelor's degree in computer science, information technology, or a related field. This education provides a solid foundation in both technology and security principles. Next, gain practical experience. Working in IT roles or internships can help you understand real-world security challenges. Experience with security tools and incident response is valuable.
- Earn a degree in computer science or information technology.
- Gain experience in IT roles or internships.
- Obtain certifications such as CISSP or CEH.
- Network with professionals in the field.
- Apply for jobs as an Information Security Officer.
Certifications enhance your qualifications. Earning certifications like Certified Information Systems Security Professional (CISSP) or Certified Ethical Hacker (CEH) shows your expertise. These credentials can make your resume stand out. Networking with professionals can provide insights into the industry and open job opportunities. Joining professional groups and attending conferences can help you connect with others in the field. Finally, apply for positions as an Information Security Officer. Tailor your resume to highlight your skills and experience. Be ready to demonstrate your ability to protect and secure information systems.
How long does it take to become a Information Security Officer?
People interested in becoming an Information Security Officer should expect a clear path with defined steps. Typically, one can enter this field with a bachelor's degree in computer science, information technology, or a related field. This journey often takes four years of full-time study. Some may choose to pursue a master's degree to enhance their credentials, adding another two years of study.
After completing formal education, gaining practical experience becomes crucial. Many professionals spend several years working in IT or related fields before specializing in information security. Internships or entry-level positions can provide valuable hands-on experience. Certifications like CompTIA Security+ or Certified Information Systems Security Professional (CISSP) can also boost career prospects. These certifications usually require passing exams, adding another layer of preparation.
In summary, the path to becoming an Information Security Officer includes:
- Four years of a bachelor's degree
- Optional two years for a master's degree
- Several years of work experience
- Obtaining relevant certifications
Information Security Officer Job Description Sample
The Information Security Officer (ISO) is responsible for developing, implementing, and managing an organization's information security program. The ISO ensures that the organization's information assets are protected against threats, vulnerabilities, and incidents by overseeing information security policies, procedures, and controls.
Responsibilities:
- Develop, implement, and maintain information security policies and procedures.
- Conduct risk assessments and vulnerability assessments to identify and mitigate potential security threats.
- Develop and implement an incident response plan to ensure a swift and effective response to security breaches.
- Ensure compliance with relevant laws, regulations, and standards related to information security.
- Manage security projects and initiatives, including security audits, penetration testing, and security training.
Qualifications
- Bachelor’s degree in Information Security, Computer Science, or related field.
- Certifications such as CISSP, CISM, or equivalent.
- Proven experience in information security management, including risk assessment and incident response.
- Strong understanding of information security frameworks and standards (e.g., NIST, ISO/IEC 27001).
- Excellent analytical and problem-solving skills.
Is becoming a Information Security Officer a good career path?
A career as an Information Security Officer promises a unique blend of challenges and rewards. This role focuses on safeguarding an organization's data and IT infrastructure from security threats. Security Officers must stay ahead of cyber threats by implementing protective measures and responding to incidents. They work in various settings, from corporate offices to IT departments.
Being an Information Security Officer offers several benefits. It provides opportunities for continuous learning and professional growth. Officers often work with cutting-edge technology and face new challenges daily. They play a crucial role in protecting sensitive data, ensuring organizational compliance, and maintaining trust with clients and stakeholders. However, this career also has its drawbacks. The job can be stressful due to the constant threat of cyber-attacks. Officers must also work long hours, especially during security incidents.
Considering the pros and cons can help in deciding if this career is the right fit. Below are some key points to keep in mind:
- Pros:
- Continuous learning and growth
- Opportunity to work with advanced technology
- Critical role in protecting sensitive data
- Essential for organizational compliance
- Cons:
- High stress levels due to ongoing threats
- Frequent need to work long hours
What is the job outlook for a Information Security Officer?
Becoming an Information Security Officer offers a promising career outlook. The U.S. Bureau of Labor Statistics reports around 54,300 job openings annually. This field is growing, with a projected increase of 14.9% from 2022 to 2032. This growth shows strong demand for qualified professionals.
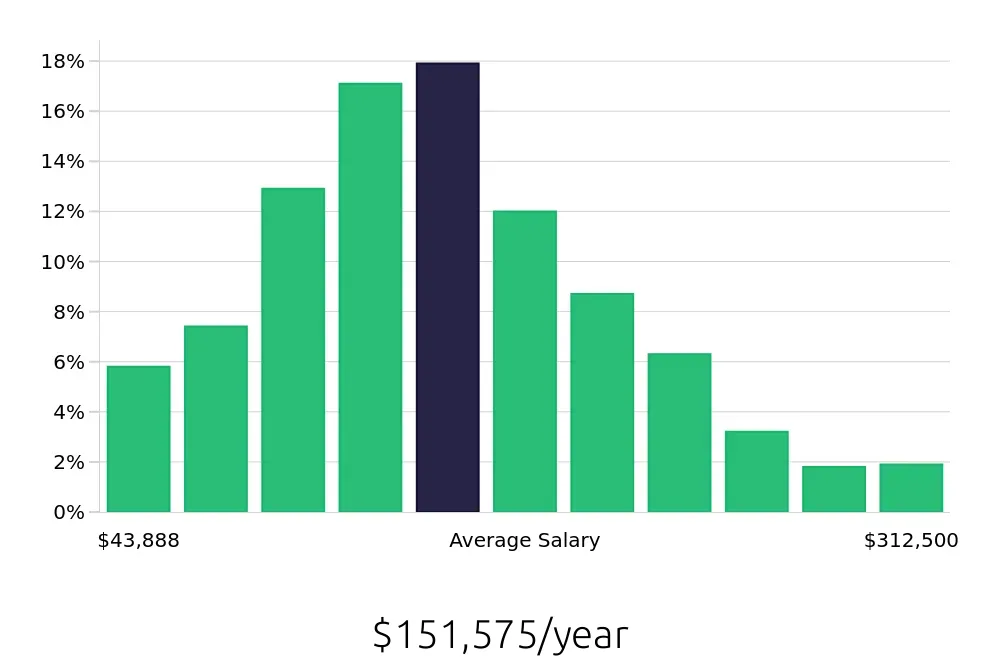
Information Security Officers play a vital role in protecting organizations from cyber threats. With companies increasingly investing in cybersecurity, the need for skilled officers is rising. This trend offers many opportunities for those entering the field. The average annual salary is $114,420, with hourly pay at about $55.01. These figures highlight the financial rewards of this career choice.
Job seekers benefit from the diverse work environments available. Roles span across various industries, including tech, finance, and healthcare. This versatility ensures a range of job options. Positions often include travel, making the work dynamic and engaging. With a strong job outlook and competitive compensation, now is an excellent time to consider a career as an Information Security Officer.
Currently 201 Information Security Officer job openings, nationwide.
Continue to Salaries for Information Security Officer