What does a Information Systems Security Manager do?
An Information Systems Security Manager plays a crucial role in protecting a company’s data and information. This position involves overseeing security measures and ensuring compliance with regulations. The manager assesses risks and implements strategies to safeguard against cyber threats.
Responsibilities often include creating and enforcing security policies, training staff on best practices, and responding to security incidents. The manager collaborates with IT and other departments to ensure that systems are secure and up-to-date. They also stay informed on the latest security trends and technologies to protect the organization’s assets. This role is vital for maintaining the integrity and confidentiality of sensitive information.
Key duties of an Information Systems Security Manager may include:
- Developing security protocols
- Conducting risk assessments
- Managing incident response plans
- Ensuring compliance with security standards
- Reporting to senior management on security status
How to become a Information Systems Security Manager?
Becoming an Information Systems Security Manager involves several steps. It requires education, experience, and certifications. Follow these steps to start your career in this field.
First, earn a bachelor's degree in computer science, information technology, or a related field. This education provides the basics needed for the job. Look for courses in cybersecurity, network security, and information systems.
- Gain Experience: Work in IT or a related field. Look for jobs in network administration, IT support, or cybersecurity. This experience helps build the skills needed for the role.
- Get Certified: Earn relevant certifications. Popular ones include Certified Information Systems Security Professional (CISSP) and Certified Ethical Hacker (CEH). These certifications show you have the skills and knowledge needed.
- Advance Your Career: Work your way up. Take on more responsibility in your current job. This can include managing a team or handling security projects. Experience in leadership roles is key.
- Network: Connect with other professionals in the field. Attend conferences, join professional groups, and use LinkedIn. Networking opens doors to job opportunities.
- Apply for Jobs: Look for Information Systems Security Manager positions. Tailor your resume and cover letter for each job. Highlight your education, experience, and certifications. Be ready for interviews and to show your skills.
How long does it take to become a Information Systems Security Manager?
Gaining the skills to manage information systems security can take a few different paths. Most start with a bachelor's degree in a related field, like computer science or information technology. This path usually takes four years. Some choose to deepen their knowledge with a master's degree, which takes an additional two years. Many find value in getting certifications. These can add another year or more, depending on study time and exam prep.
Job seekers should focus on building practical experience. Internships, entry-level IT jobs, or volunteering in security roles can help. This hands-on work builds skills and makes resumes stronger. Many employers value certifications, such as Certified Information Systems Security Professional (CISSP) or Certified Information Security Manager (CISM). These add another layer of expertise and can take time to earn, often needing several months to a year. Real-world experience and credentials together open doors to advanced positions. Patience and dedication pay off, as this journey can span five to seven years, setting a solid foundation for a rewarding career.
Information Systems Security Manager Job Description Sample
An Information Systems Security Manager is responsible for overseeing the security of an organization's information systems and data. This role involves implementing security measures, managing security incidents, and ensuring compliance with relevant laws and regulations.
Responsibilities:
- Develop and implement security policies and procedures to protect information systems and data.
- Conduct risk assessments and vulnerability testing to identify potential security threats.
- Manage and coordinate security incident response efforts.
- Monitor and analyze security logs and reports to detect and respond to security breaches.
- Ensure compliance with relevant laws, regulations, and industry standards.
Qualifications
- Bachelor's degree in Information Technology, Computer Science, Information Security, or a related field.
- Certifications such as CISSP, CISM, or CEH are highly desirable.
- Minimum of 5-7 years of experience in information security management.
- Strong knowledge of security frameworks, such as ISO 27001, NIST, and GDPR.
- Experience with security incident response and risk management.
Is becoming a Information Systems Security Manager a good career path?
An Information Systems Security Manager plays a crucial role in protecting an organization's data and systems. This career requires a mix of technical skills, strategic planning, and leadership. They ensure that security policies are in place and followed. This professional also monitors systems for security breaches and threats. They train staff on security measures and work to fix vulnerabilities.
Working as an Information Systems Security Manager offers several benefits. This role provides a stable job with good pay. It also offers opportunities to make a real difference by protecting important information. The job often includes benefits like health insurance and retirement plans. However, it can be stressful, as managers must stay alert to new threats constantly. The job can also require working long hours, especially during a security crisis. Another challenge is keeping up with rapidly changing technology.
Here are some pros and cons of this career:
- Pros:
- Stable job with good pay
- Opportunity to protect important data
- Good benefits, like health insurance
- Chances for career growth and advancement
- Cons:
- Job can be stressful
- May need to work long hours
- Must keep up with new technology
What is the job outlook for a Information Systems Security Manager?
Information Systems Security Managers play a vital role in safeguarding organizations from cyber threats. This role is in high demand and expected to grow over the next decade. The Bureau of Labor Statistics (BLS) reports an average of 40,200 job openings each year. The outlook for this role is promising, with a projected 4% increase in job openings from 2022 to 2032. Securing a position in this field can offer stability and growth opportunities.
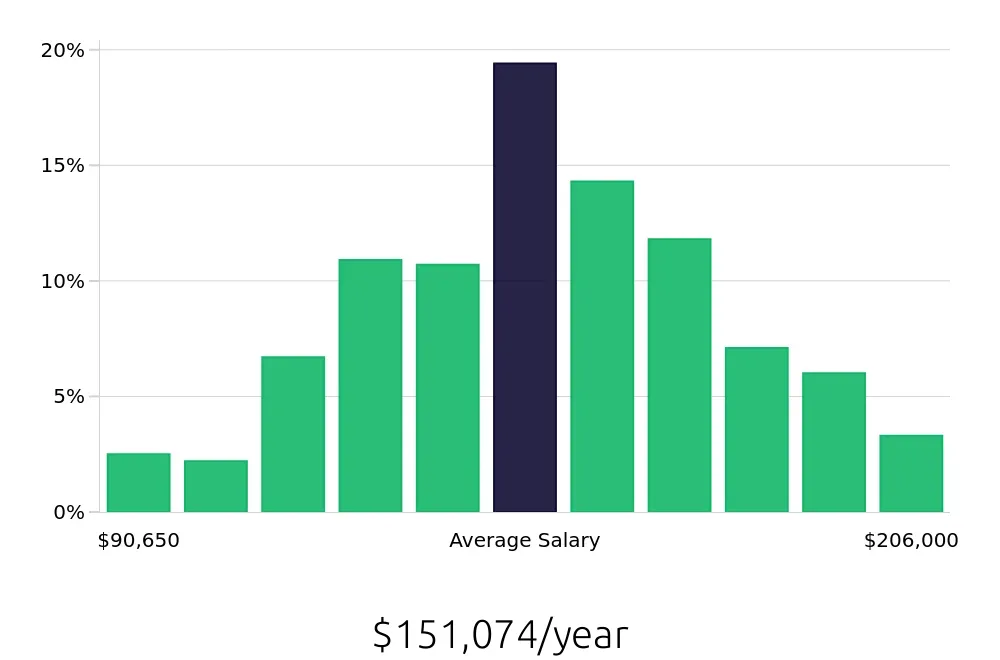
The BLS also highlights the compensation for Information Systems Security Managers. On average, they earn an annual salary of $113,710 nationwide. This role also offers competitive hourly wages, with an average of $54.67 per hour. These figures reflect the value organizations place on skilled professionals who can protect sensitive data and IT infrastructure. Aspiring candidates can expect a rewarding career with both job security and financial benefits.
For job seekers, this trend indicates a positive job market for Information Systems Security Managers. With consistent demand and solid compensation, this career path offers a promising future. Individuals who pursue this role can look forward to a stable career and the chance to make a significant impact in cybersecurity.
Currently 74 Information Systems Security Manager job openings, nationwide.
Continue to Salaries for Information Systems Security Manager