What does a Security Architect do?
A Security Architect designs and implements security measures for an organization. They analyze the security needs and identify potential risks. They create security plans and policies to protect the company's information and assets. This role involves working closely with IT teams to ensure all systems meet security standards. They also train employees on best practices for maintaining security.
The Security Architect constantly updates security strategies to keep up with new threats. They perform regular security audits and tests to ensure everything is working as it should. They also develop incident response plans in case of a security breach. This role requires a deep understanding of cybersecurity principles and technologies. It is a critical position that helps safeguard an organization from potential cyber threats.
How to become a Security Architect?
Becoming a Security Architect involves a clear path of education, experience, and skill development. This role requires expertise in both information security and architectural design. By following a structured process, individuals can position themselves for success in this critical field.
Here are five key steps to becoming a Security Architect:
- Earn a relevant degree. Most employers require at least a bachelor's degree in computer science, information technology, or a related field. This provides a solid foundation in both technical skills and theoretical knowledge.
- Gain experience in information security. Work in roles that focus on protecting computer systems and networks. This could be as a security analyst, network administrator, or IT manager. Real-world experience is valuable and often required.
- Pursue certifications. Professional certifications like CISSP (Certified Information Systems Security Professional) and CISM (Certified Information Security Manager) enhance credibility and knowledge. They demonstrate a commitment to the field.
- Develop architectural skills. Learn about system design and architecture. Understanding how to design secure systems and networks is crucial. This can involve taking courses, attending workshops, or working on projects that require architectural thinking.
- Build a strong professional network. Connect with other professionals in the field. Networking can lead to job opportunities, collaborations, and valuable insights. Attend industry conferences, join professional organizations, and participate in online forums.
How long does it take to become a Security Architect?
The journey to becoming a Security Architect demands dedication and hard work. Most professionals find it takes several years to reach this advanced role. On average, it can take 5 to 10 years of experience in related fields to qualify. This timeline includes a mix of education, practical experience, and continuous learning.
Typically, it starts with earning a bachelor's degree in computer science, information technology, or a related field. Alongside this, gaining hands-on experience through internships or entry-level positions is essential. Many Security Architects also pursue certifications like CISSP (Certified Information Systems Security Professional) to enhance their skills. Real-world experience in roles like security analyst, network engineer, or systems administrator can take 3 to 5 years. After gaining the necessary experience, individuals can step into a Security Architect position, continually updating their knowledge to stay ahead in the rapidly evolving field of cybersecurity.
Security Architect Job Description Sample
We are seeking a highly skilled Security Architect to develop and implement robust security frameworks to safeguard our company's data and systems against potential threats. This role requires a strategic approach to security, with a focus on both preventive and reactive measures. The ideal candidate will have a deep understanding of cybersecurity principles and best practices, along with the ability to communicate complex security concepts to non-technical stakeholders.
Responsibilities:
- Design, implement, and manage comprehensive security architectures for the company's IT infrastructure.
- Conduct risk assessments and security audits to identify vulnerabilities and potential threats.
- Develop and enforce security policies and procedures to protect against data breaches and cyber-attacks.
- Collaborate with IT and business leaders to integrate security measures into the overall IT strategy.
- Stay updated on emerging security trends and technologies, and recommend improvements to existing security frameworks.
Qualifications
- Bachelor’s degree in Computer Science, Information Technology, or a related field; Master’s degree preferred.
- Certified Information Systems Security Professional (CISSP) or equivalent certification.
- Minimum of 7-10 years of experience in a security-focused role, with at least 3 years in a Security Architect position.
- Proven experience in designing and implementing security architectures for complex IT environments.
- Strong understanding of network security, cloud security, and mobile security.
Is becoming a Security Architect a good career path?
A Security Architect plays a crucial role in protecting an organization's information assets. This role involves designing and implementing security systems to guard against threats. Security Architects work with different teams to ensure security measures align with business needs. They often need to stay updated with the latest trends in cybersecurity. This career offers a mix of technical skills and strategic planning, making it both challenging and rewarding.
Choosing this career path brings many benefits. Working as a Security Architect often includes a competitive salary and the chance to make a significant impact on an organization's security posture. This role also provides opportunities for continuous learning and professional growth. However, the job can be demanding, often requiring long hours, especially during a security breach. The need to stay current with rapidly evolving threats can also be stressful. Balancing technical expertise with business objectives requires a unique skill set.
Here are some pros and cons to consider:
- Pros:
- Competitive salary
- Opportunities for career advancement
- Variety of work environments
- Continuous learning opportunities
- Cons:
- High stress levels
- Long working hours
- Need for continuous education
- High responsibility
What is the job outlook for a Security Architect?
The job outlook for Security Architects looks strong and promising. Each year, approximately 54,300 job positions become available. This trend shows a steady demand for skilled professionals in this field. With the rise of cybersecurity threats, organizations need experts to protect their sensitive data. This demand ensures a stable career path for those in this role.
According to the Bureau of Labor Statistics (BLS), job openings for Security Architects are expected to grow by 14.9% from 2022 to 2032. This significant increase highlights the growing importance of cybersecurity in today's digital world. Companies are investing more in security measures to safeguard their information. This growth offers many opportunities for job seekers to enter or advance in this field.
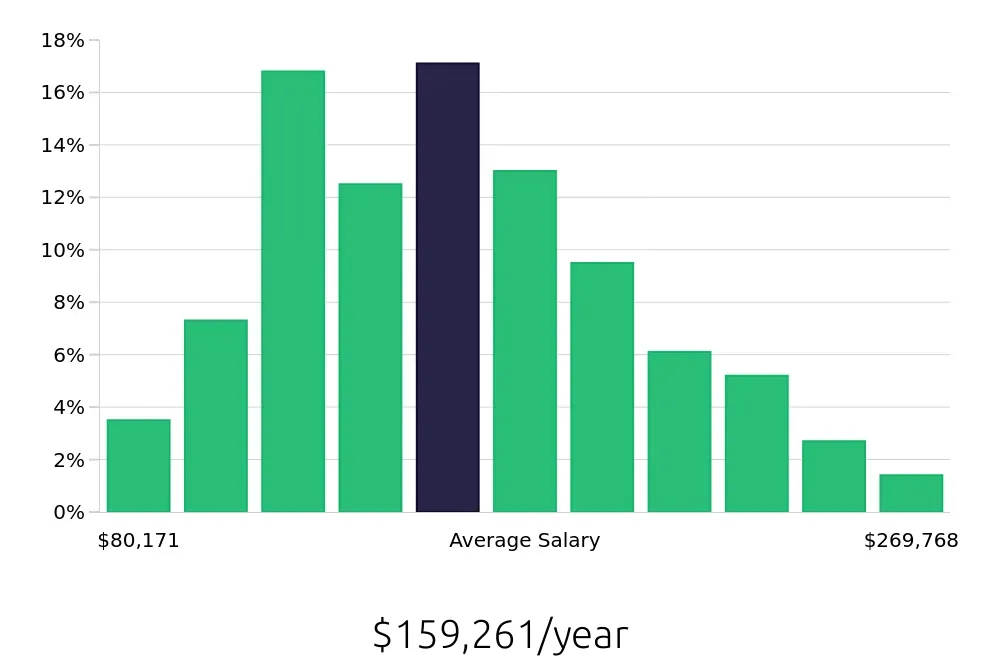
Security Architects enjoy competitive salaries as well. The average national annual compensation stands at $114,420, with an hourly rate of $55.01. These figures reflect the high value placed on cybersecurity expertise. Successful candidates can expect rewarding career prospects both in terms of job security and financial compensation. This makes the role of a Security Architect both challenging and rewarding.
Currently 128 Security Architect job openings, nationwide.
Continue to Salaries for Security Architect